Managed Patching, Vulnerability Management, and vCISO One operating model for Los Angeles, Chicago, and Phoenix
Get managed patching, vulnerability management, and vCISO oversight from one accountable team. Cut tool sprawl and close risk faster. Free cybersecurity assessment, or call your local IT lead.
Attackers are not waiting for your next maintenance window. Across Southern California, Chicagoland, and Arizona, mid-market and multi-site organizations are facing the same problem: more critical flaws, shorter exploit timelines, and lean IT teams that cannot triage every Microsoft, Cisco, Adobe, Oracle, Fortinet, Palo Alto, Ivanti, Apple, Google, and Linux advisory by hand.
BTI Communications Group is a modern, state-of-the-art MSP that treats managed patching, vulnerability management, and vCISO as one operating model, not three disconnected projects. You get faster identification of what matters, a clear patching strategy, verified closure, executive oversight, and measurable savings on tools, labor, and downtime, with better cybersecurity as the baseline, not the only benefit.
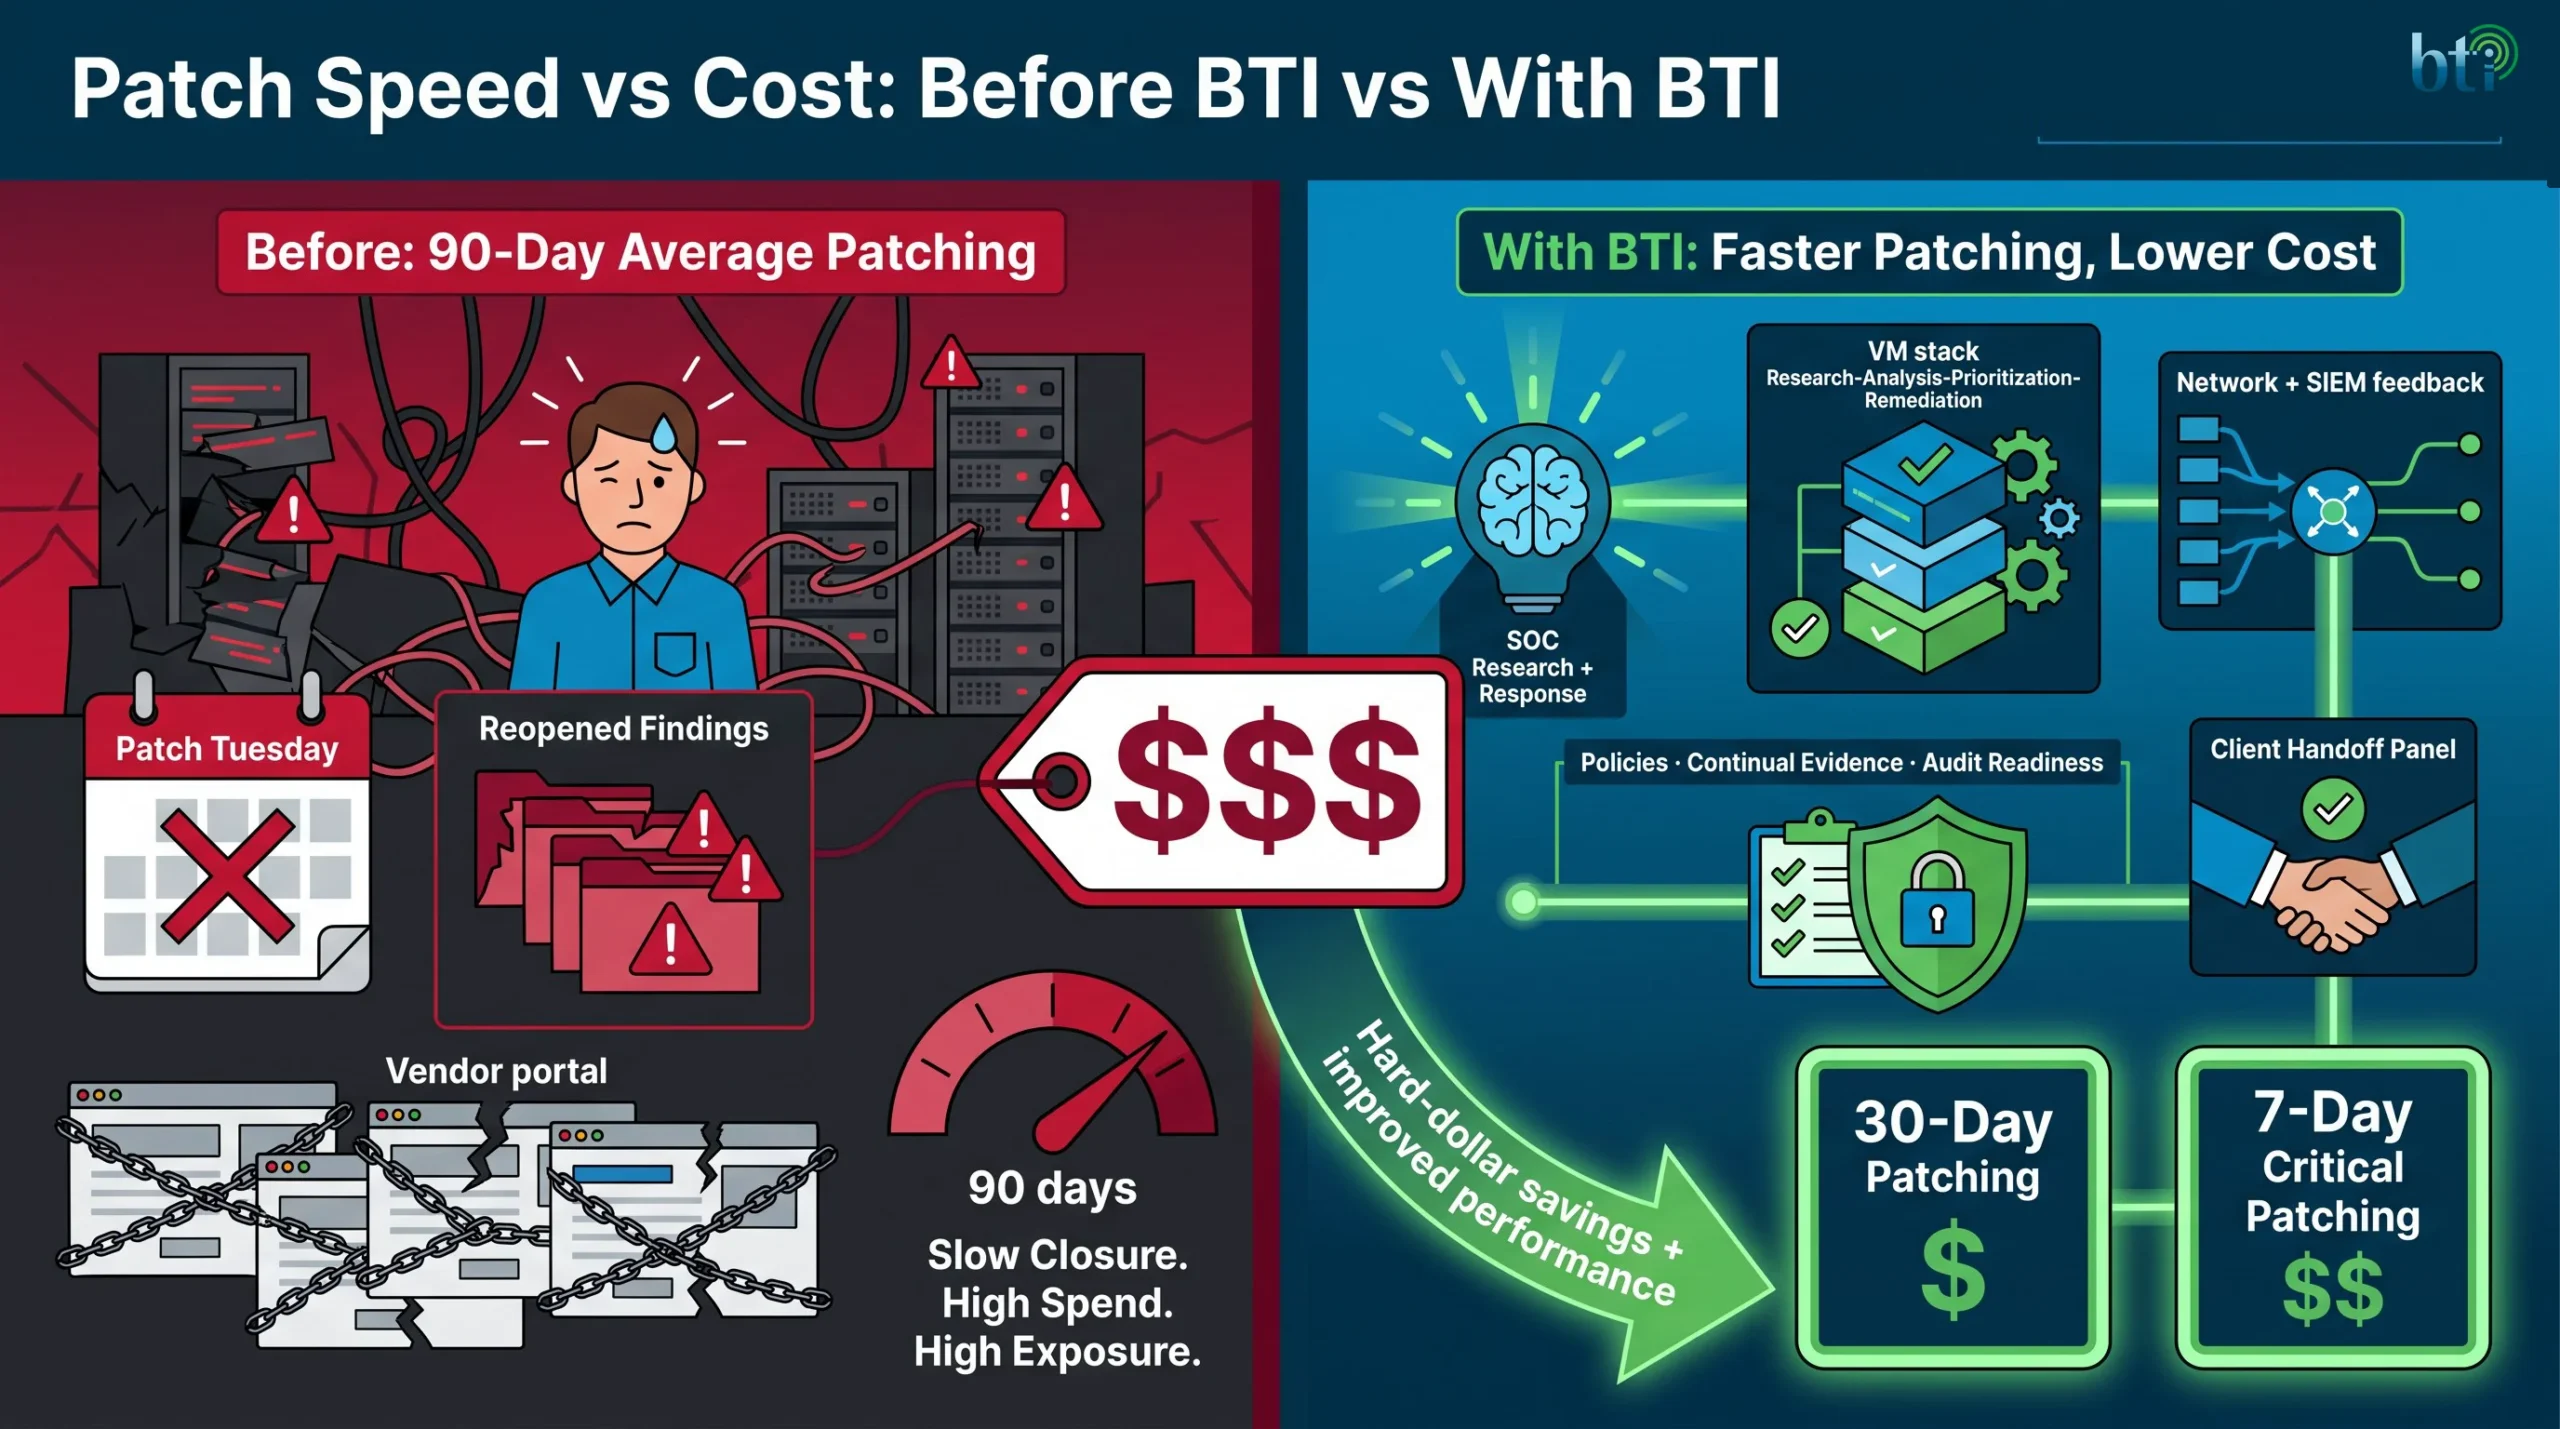
A traditional SLA tracks ticket times and uptime. A Protection Level Agreement locks a measurable protection outcome and its cost, with patching intervals written into the agreement. In Proctor's illustrative enterprise cost ladder, about $1 million per year funds 30-day critical patching, about $2 million funds 15-day, and about $5 million funds 7-day. Mid-market firms in Los Angeles, Chicago, and Phoenix still need that same clarity: pick an interval you can defend, fund a program that can hit it, and staff it with humans and AI working around the clock. BTI is built to deliver comparable protection outcomes without the seven-figure enterprise PLA price tag.
The internet is under attack. Patch everything that matters, fast.
CISA’s Known Exploited Vulnerabilities (KEV) catalog and major vendor advisories from late September through mid-October 2026 show the same pattern: edge appliances, email gateways, VPN portals, collaboration platforms, browsers, and Windows endpoints are being hit while many organizations still rely on monthly “best effort” patching.
If a product is internet-facing or widely deployed in your offices, warehouses, clinics, plants, or remote workforce, assume someone is scanning for it. “We’ll get to it next quarter” is how breaches start.
For the leadership view of why fundamentals beat shiny tools, read Vulnerability Management Before AI. For how governed AI can help lean teams keep up safely, see Governed AI for patching, MFA, and security keys.
Recently disclosed or KEV-listed vulnerabilities (≈ Sept 22-Oct 22, 2026)
Verified from CISA alerts, NVD/MSRC, and vendor advisories. Prefer actively exploited and widely deployed products. Dates are disclosure or KEV-add dates as noted.
CVE / ID
Vendor / product
Risk in plain English
Approx. date
Advisory
CVE-2026-88771
Citrix NetScaler ADC / Gateway
Unauthenticated remote code execution on edge appliances; exploited as a zero-day
This list is a sample of what a real program must track every week. Oracle’s October 2026 Critical Patch Update alone spanned a large multi-product release cycle (Oracle CPU October 2026). Without inventory, prioritization, patch windows, and verified closure, the queue never clears.
Not sure which of these affect you?Get a free cybersecurity assessment and we will map exposure, patching gaps, and the fastest risk reductions.
What managed patching + vulnerability management + vCISO means at BTI
BTI runs these as one cohesive service from a state-of-the-art MSP, not a scanner license and a slide deck.
Managed patching
We inventory endpoints, servers, network devices, and key applications; schedule patch windows; deploy OS and third-party updates; handle exceptions with compensating controls; and confirm results. Related reading: Patch your computers to reduce risk.
Vulnerability management with verified closure
We scan on a cadence (and after major changes), prioritize by known exploitation and business impact, remediate or document exceptions, then rescan to prove the finding is gone. That is the difference between activity and risk reduction. See also benefits of a vulnerability assessment and penetration testing vs vulnerability scanning.
vCISO
A vCISO gives you executive-level security leadership without a full-time hire: risk prioritization, board-ready reporting, policy and roadmap, vendor and audit readiness support, and alignment of patching and vulnerability work to business goals. CMMC and other compliance work is completed and contracted by BTI and its partners, including top industry professionals in each category. For auditor expectations, see what IT compliance auditors want to see.
Delivery models that fit your team
Fully managed / outsourced:Outsourced IT with vulnerability management and 24/7 SOC.
You get a working operating cycle: inventory, scan, prioritize, patch, verify, monitor, and report. Leadership sees open risk trending down, not a PDF of unread CVEs.
Cost and time savings
Fewer emergency weekends. Fewer “all hands” fire drills after a KEV hit. Faster mean time to remediate critical and internet-facing findings. Less time spent arguing about which ticket is really closed.
Tool and SaaS software savings
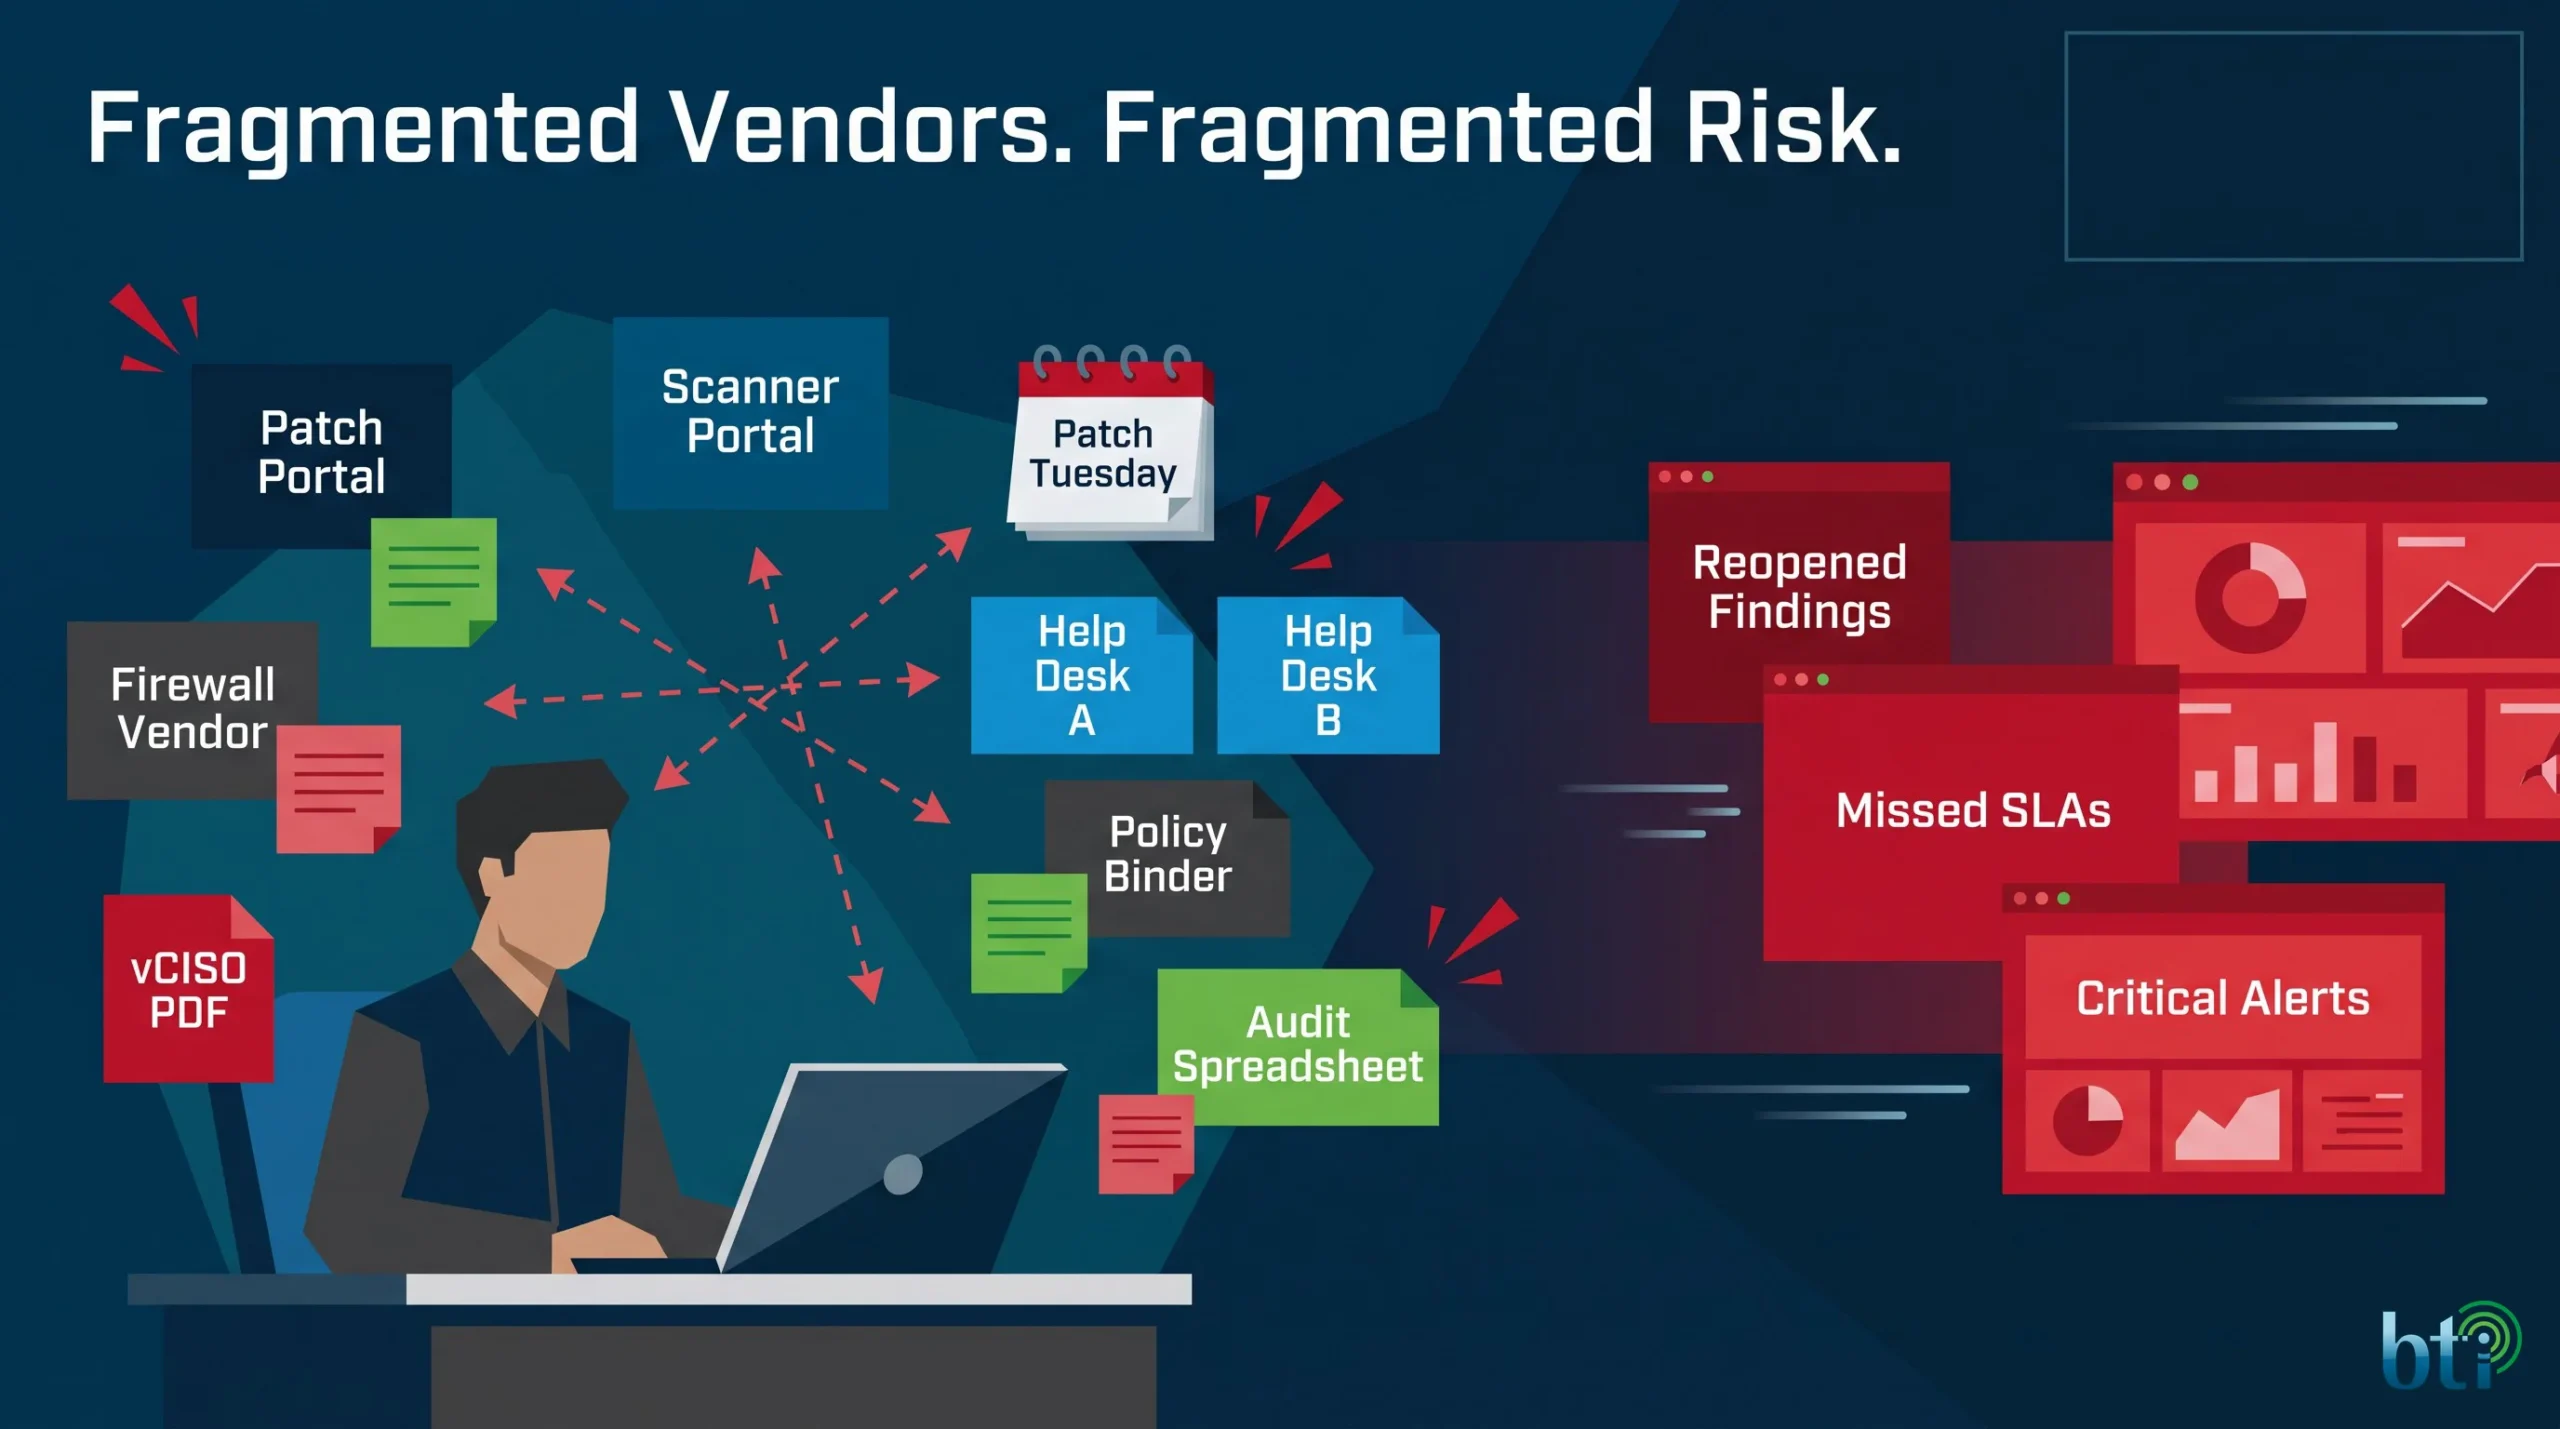
Many mid-market stacks sprawl across overlapping vulnerability scanners, patch tools, reporting add-ons, and point consultants. BTI consolidates the operating model so you are not paying three vendors to produce three incompatible dashboards. Where governed AI helps triage and track work safely, Find Out About BTI’s Governed AI Services.
Labor savings
Your team stops burning senior engineers on repetitive triage and status chasing. BTI technicians own remediation tracking and verified closure; your people focus on projects and exceptions that need institutional knowledge. For lean IT specifically, see how governed AI supports faster patching and identity hygiene.
Better cybersecurity
Shorter exposure windows on actively exploited flaws. Continuous coverage instead of annual audit panic. 24/7 detection through our SOC 2 Certified NOC/SOC when something slips through before a patch lands.
Faster, more effective identification of vulnerabilities and patching strategies
We prioritize by known exploitation, internet exposure, and business criticality, not CVSS alone. That produces a strategy your CIO, CFO, and site managers can understand: what to fix this week, what can wait, and what needs a compensating control.
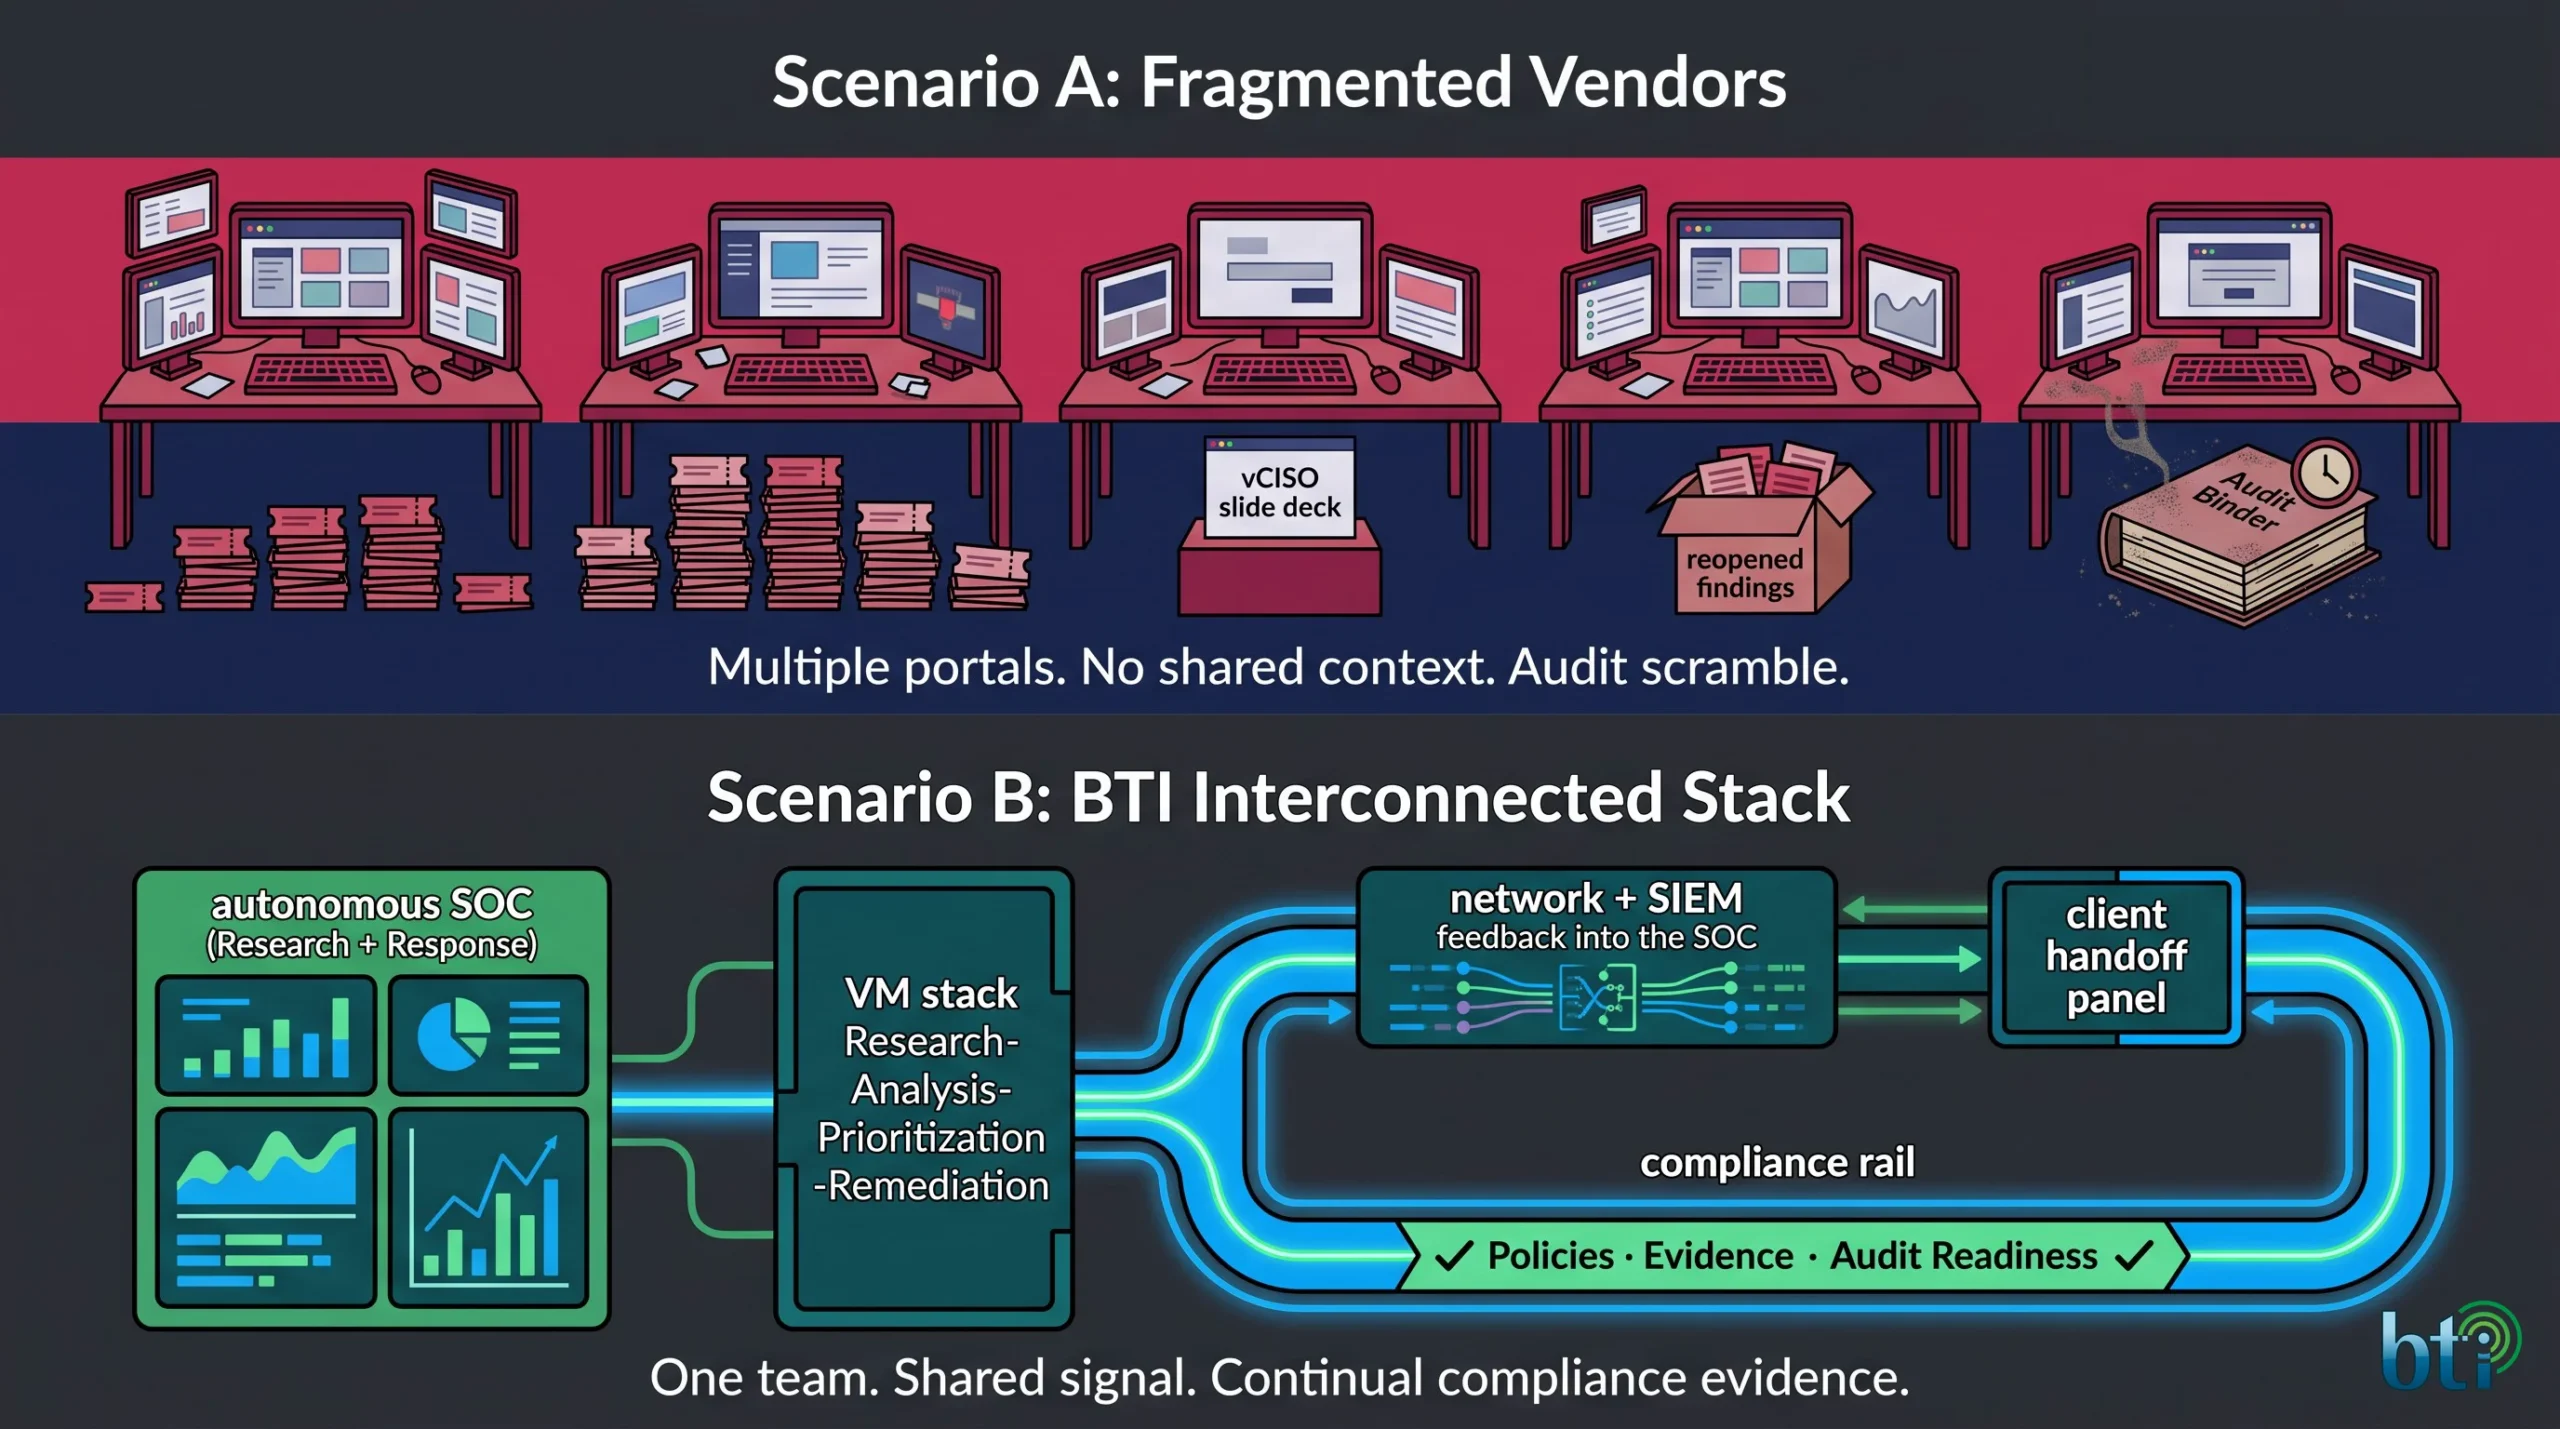
One correlated stack beats a pile of siloed tools
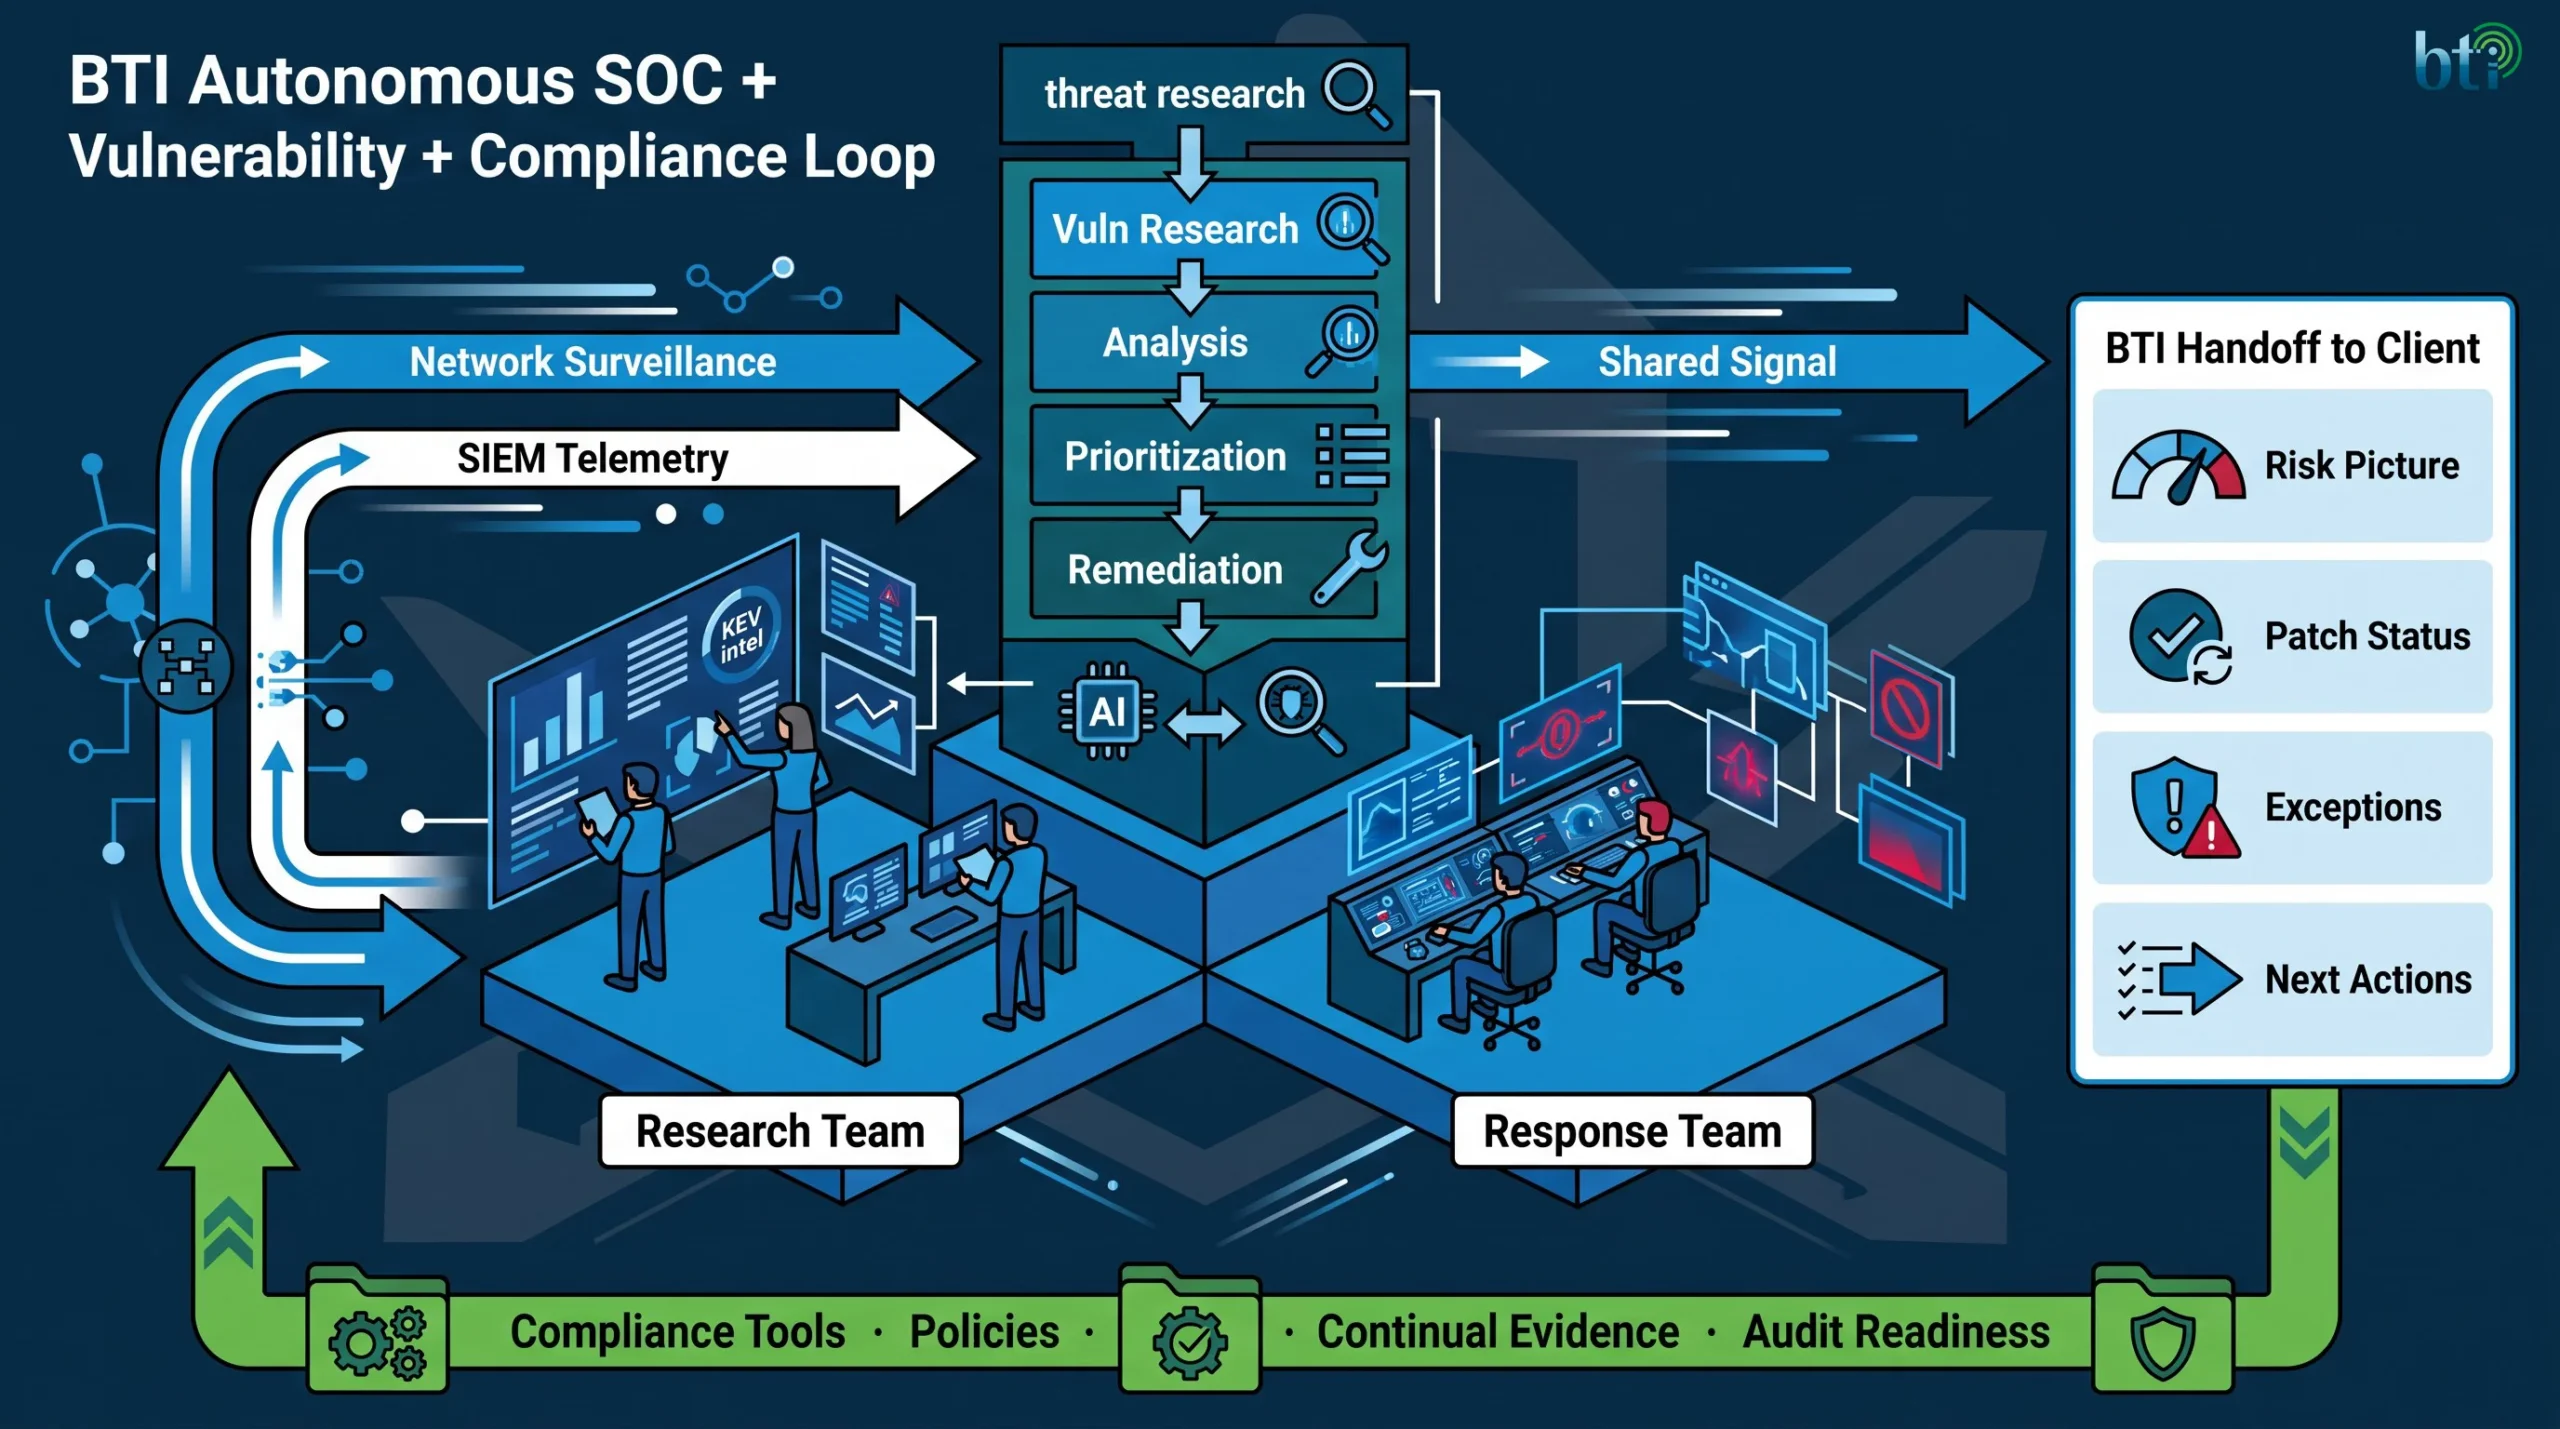
Managed patching and vulnerability management get faster and cheaper when they sit inside a correlated technology stack, not a jumble of disconnected products. BTI designs the program so AI-governed and AI-enabled operations, security monitoring, identity, communications, and physical security feed the same operating picture your technicians and leaders use to decide what to patch, what to investigate, and what to escalate.
What is interconnected at BTI
AI-powered RMM and vulnerability scanning / management at the center: asset inventory, patch status, scan findings, and remediation tracking in one operational view watched over by BTI
SOC, SIEM, and MDR for 24/7 detection and response that shares context with patching priority (what is exploited, what is exposed, what is already noisy)
Network security (firewall, IPS, browser and email controls, and related edge defenses) so internet-facing risk and internal lateral movement show up alongside CVE queues (network security)
Identity-managed systems and zero trust patterns: MFA, password management, privileged account management, and least privilege across email, browsers, remote access, and admin paths (zero trust network architecture, cybersecurity services)
Cross-correlation that changes outcomes
Signals do not stay in their lane. BTI coalesces them so a dark web password exposure, a privileged account without MFA, a firewall IPS hit, a mailbox anomaly, a browser exploit attempt, an open critical CVE on an internet-facing host, and an access-control or camera event can be related, not treated as six unrelated tickets.
That correlation is the practical benefit of one pane of glass versus siloed tools:
Built for mid-market and multi-site organizations with lean IT: manufacturing and logistics hubs, professional services, education, government, construction, nonprofits, parking and venues, critical infrastructure operators, and regulated industries that need evidence, not slogans.
Assess and inventory. Free cybersecurity assessment to baseline assets, scanning coverage, open critical/high findings, and patching cadence.
Prioritize by real risk. Map CISA KEV, vendor advisories, and internet exposure to *your* estate.
Operate the cycle. Scan, patch, remediate, document exceptions, verify closure, and report.
Monitor 24/7. SOC 2 Certified NOC/SOC watches for activity that arrives before a fix can.
Govern with vCISO. Roadmap, metrics, and executive communication so security stays a managed program.
Engagements typically start with an assessment, then a fixed-scope or managed monthly model based on sites, user count, and whether you want fully managed or co-managed delivery. Price ranges depend on scope; we quote after we see the environment rather than inventing list prices.
Proof and trust
Over 40 years supporting organizations with technology and security operations
SOC 2 Certified NOC/SOC with 24/7 monitoring and SIEM-backed response
ISO 27001 compliant practices and audit-minded evidence habits
CMMC and related compliance work completed and contracted by BTI and its partners, including top industry professionals in each category
Anonymous mid-market pattern we see repeatedly: once verified closure and KEV prioritization are in place, open critical aging drops and audit prep stops being a scramble
What is the difference between vulnerability scanning and vulnerability management?
Scanning finds weaknesses. Management owns the full cycle: prioritization, remediation or compensating controls, verified closure, reporting, and continuous improvement. See penetration testing vs vulnerability scanning.
What is a Protection Level Agreement (PLA), and how is it different from an SLA?
An SLA measures service delivery (for example, uptime or ticket response). A PLA, as Gartner’s Paul Proctor describes it, is a business decision that pairs a measurable protection outcome with its cost, most famously, how many days critical systems may remain unpatched. Proctor puts it bluntly: “How many days would you like your systems available for hacking?” See also Gartner’s CFO press release on PLAs and outcome-driven metrics. BTI helps you set a realistic patching interval and then operate the managed patching, vulnerability management, and vCISO program to meet it.
Do we need a vCISO if we already have managed patching?
If leadership needs risk prioritization, board reporting, and a multi-quarter roadmap tied to audits and insurance questions, yes. Patching without executive ownership often stalls on exceptions and budget. Explore vCISO.
How fast should we patch actively exploited vulnerabilities?
Treat CISA KEV and internet-facing criticals as emergency work outside the normal monthly cycle. Federal agencies often have multi-day remediation windows; commercial teams should move just as fast when exposure is real.
Will this replace our existing security tools?
Often we reduce overlap and noise. Sometimes we keep what works and change the operating model. The goal is fewer tools doing more of the right work, with clear ownership.
Do you serve only Los Angeles, Chicago, and Phoenix?
Those are our core markets with local teams and phone lines. We also support multi-site and national organizations from that footprint with remote operations and on-site where needed.
The last month’s advisories are not an anomaly. They are the operating tempo. Mid-market teams in Los Angeles, Chicago, and Phoenix that win treat managed patching, vulnerability management, and vCISO as one program with verified closure and clear ownership.
Get a free cybersecurity assessmentTalk to our cybersecurity teamCall local IT sales: LA 323-510-8003 · Chicago 312-492-2613 · Phoenix 480-272-8728
What Our Clients Say About BTI’s Managed IT and Security Services
Jonathon Huff
★★★★★
The Moody Church
BTI consistently solves IT challenges that our staff doesn't have the skill or time for. Their installation team is excellent and their support always makes sure all of our issues are solved.
Rebecca Gadomski
★★★★★
Edgewood Clinical
BTI has been exactly what our growing company has needed for so long! They provide friendly, professional service and have consistently been willing to go above and beyond to ensure our complete satisfaction.
Dave Tourje
★★★★★
Alpha Structural, Inc.
The entire team at BTI has exceeded my expectations. They took my company to the technology and security level I needed.
Contact Us Today for a Free Consultation Strengthen Your Business.
BTI’s managed patching, vulnerability management, and vCISO services scale with you, helping your team stay productive, protected, and prepared for what’s next.
Let’s Talk IT. Book your free consultation today.