Over 40 Years in BusinessISO 27001 compliantPublic sector: GSA contract holder

LA 562-298-5000 · Chicagoland 312-432-5300 · Phoenix 602-733-6807 · Client Support

BTI Orange County (served from Santa Fe Springs): Orange County hub · Access control · Security cameras · Managed IT · Cybersecurity · Brivo Eagle Eye video · Anaheim IT · Los Angeles hub
Orange County, served from our Santa Fe Springs office

Cybersecurity Services in Orange County

Managed detection and response, email security, MFA, patching, backups and testing for Orange County businesses that need to stop ransomware, pass customer audits and answer cyber insurance questionnaires. Start with a free consultation and a free pen test.

  • Free consultation and pen test
  • 24/7 NOC/SOC
  • ISO 27001 compliant governance
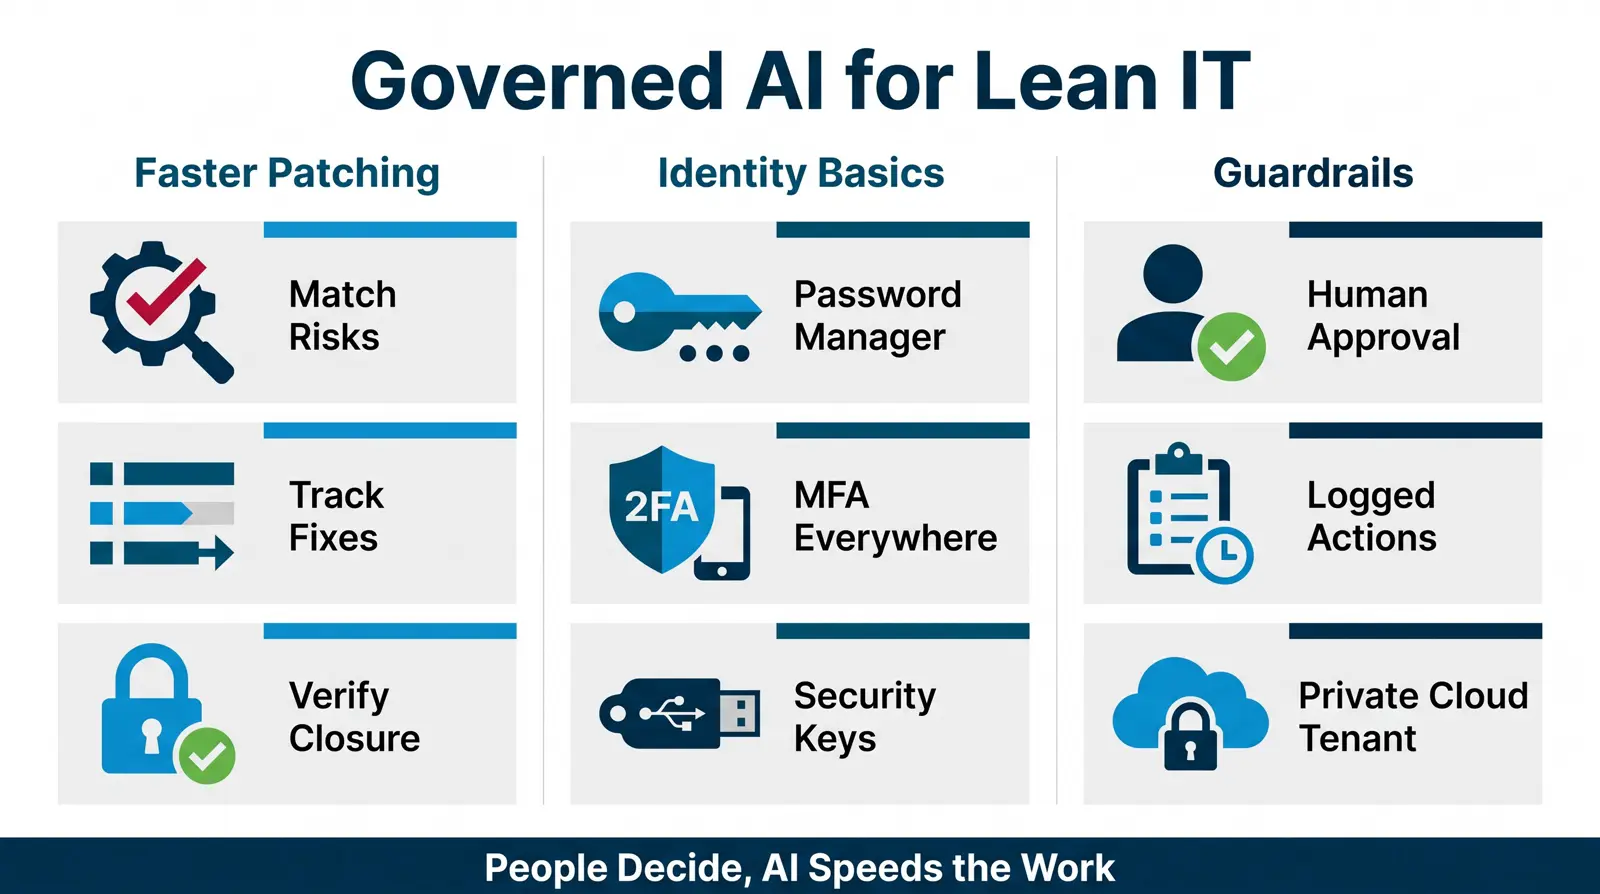
Security keys and MFA prompts illustrating governed patching and identity security

The short answer

BTI Communications Group, LTD. provides managed cybersecurity to Orange County businesses from its Santa Fe Springs office, and has been in business for over 40 years. Our 24/7 NOC/SOC runs detection and response, email security, identity protection, patching and backups, and penetration testing is run with our independent testing partner. Call 562-298-5000 or request a free consultation and pen test.

Over 40 years in business24/7 NOC/SOCISO 27001 compliant400+ engineersGSA contract holder

On this page: Free pen testLocal threatsSecurity layersCompliance and insuranceGetting startedCities servedFAQ

Free consultation and pen test

A BTI engineer reviews your risks, compliance needs and insurance requirements with you. Then we run a credential-free Level 1 penetration test of 3 to 5 machines you choose, with our independent testing partner.

  • A plain language report with every finding ranked
  • A roadmap for what to fix now, what to plan and what to monitor
  • No cost and no obligation

Request my free pen test

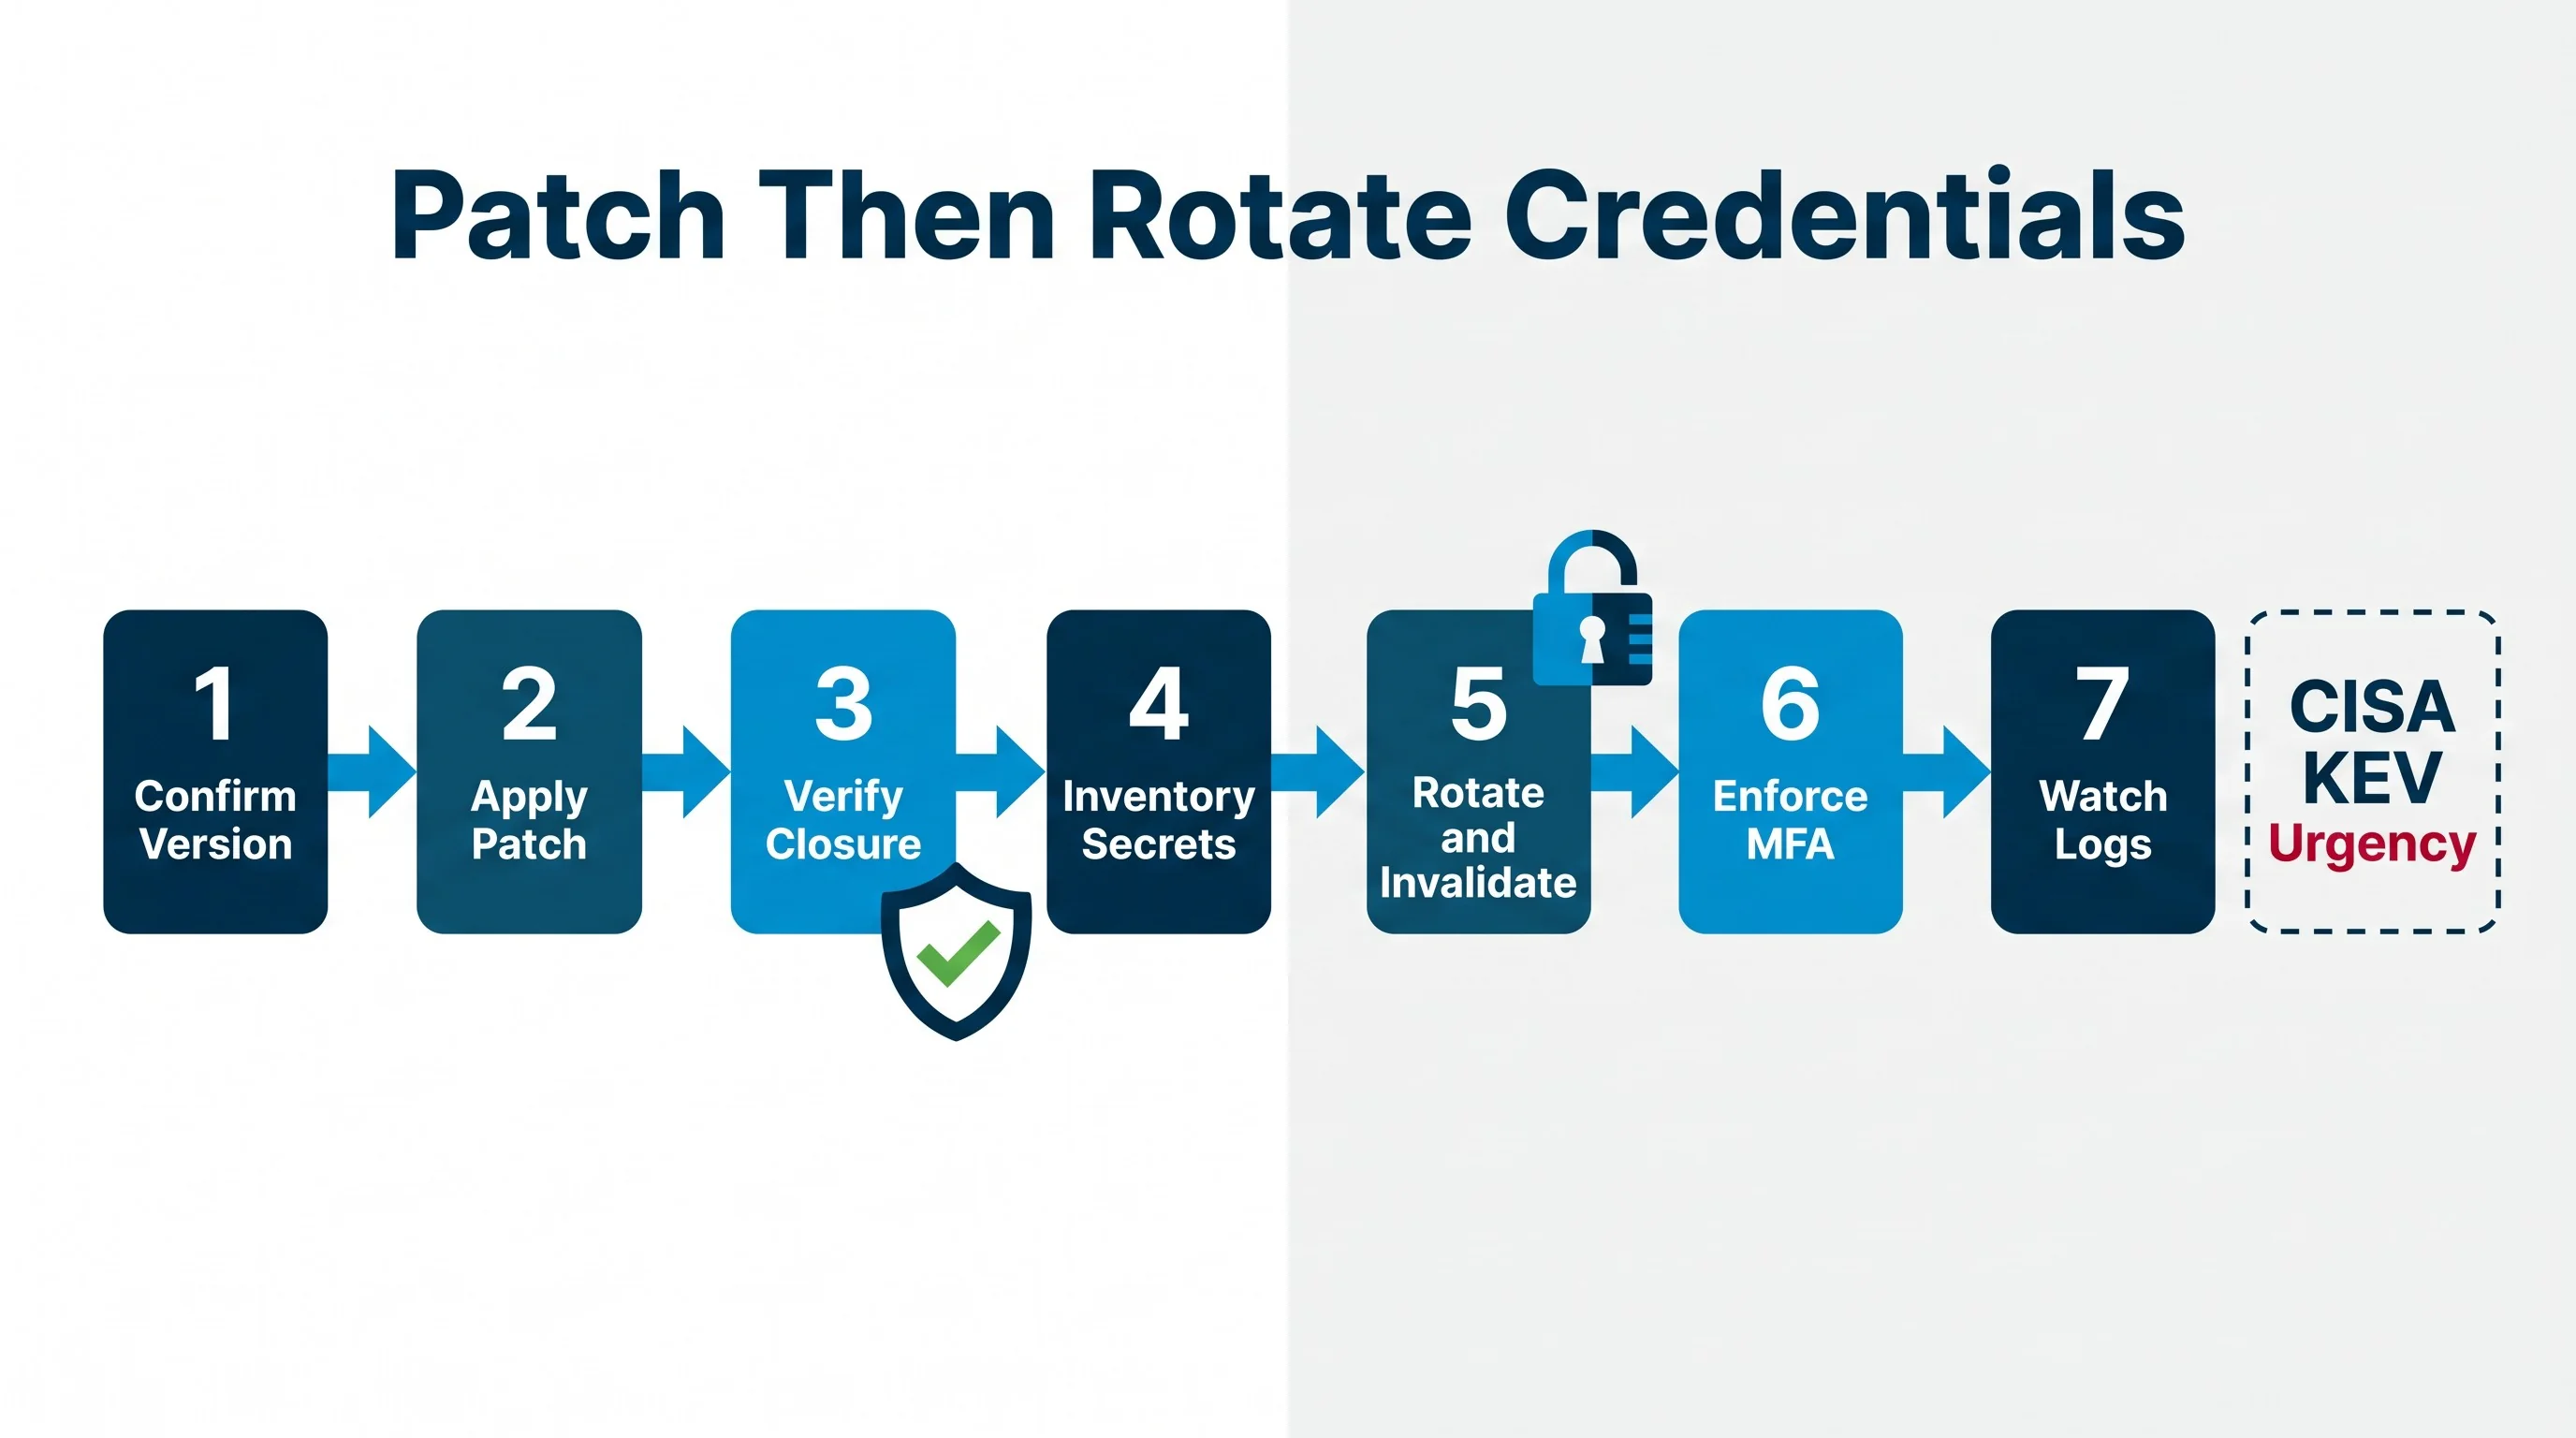
Credential rotation after critical vulnerabilities are found
Findings turn into a ranked list of fixes.

What Orange County businesses are up against

Ransomware

Attackers target firms that hold client data or cannot stop production: accounting and law firms, insurers, manufacturers and medical groups. Detection and tested backups decide whether an attack is an incident or a shutdown.

Business email compromise

Fake invoices and wire change requests hit finance teams and title, escrow and real estate offices. Email filtering, MFA and staff training stop most of them.

Customer and supply chain audits

Aerospace, defense and medical device suppliers are asked to prove controls before they win or keep contracts. CMMC and other compliance work is completed and contracted by BTI and its partners, including top industry professionals in each category.

Cyber insurance renewals

Carriers ask about MFA, endpoint detection and response, backups and training before they renew. Gaps mean higher premiums or exclusions.

Remote and hybrid work

Laptops leave the office every day. Device management, identity protection and secure access keep company data safe off the network.

Building systems on the network

Cameras, door controllers and other IoT devices are often the least protected computers a company owns. See IoT security.

The security layers we run for Orange County clients

LayerWhat it doesLearn more
Managed detection and responseWatches endpoints and cloud accounts around the clock and isolates threats.MDR
Managed SIEMCollects and correlates logs for detection and audit evidence.Managed SIEM
Email security and trainingFilters phishing and trains staff with simulated attacks.Email security and awareness training
Identity and device securityMFA, conditional access and device management.Identity and device security
Endpoint protectionNext generation antivirus and control of what runs on each device.Endpoint protection
Network securityFirewalls, DNS filtering, network access control and SASE.Network security
Patching and vulnerability managementUpdates and scans tracked to closure, with vCISO oversight.Patching and vulnerability management
Testing and evidenceOngoing testing by an independent testing partner, with Cyber Liability Essentials and Cyber Watch plans.Cyber Liability Essentials and Cyber Watch
vCISO and governancePolicies, risk reviews and board level reporting.vCISO services

Compliance and cyber insurance support

Most Orange County clients come to us with a deadline: an insurance renewal, a customer questionnaire or an audit. We map the controls you have against what is being asked and close the gaps in order.

  • Cyber insurance questionnaires: MFA, EDR, backups, training and incident response
  • CCPA and CPRA data protection practices for California businesses
  • California breach notification readiness under Civil Code 1798.82
  • PCI DSS for businesses that take cards
  • NIST based programs and CMMC readiness for defense suppliers

See cyber insurance readiness and governance, risk and compliance. Our own practices follow ISO 27001 compliant governance, independently reviewed through the TAG ISO 27001 Compliance Program.

Email protection shield over an inbox
Email is still where most attacks start.

A ransomware readiness checklist for Orange County businesses

Use this list to check your own environment. Each unchecked item is a common way attacks succeed.

  • MFA on email, remote access and every admin account
  • Endpoint detection and response on every computer and server
  • Email filtering for phishing and impersonation
  • Backups that are offline or immutable, with a tested restore in the last quarter
  • Patching for operating systems, browsers and firewalls on a schedule
  • Admin rights removed from everyday user accounts
  • A written incident response plan with phone numbers that work when email is down
  • Security awareness training with phishing simulations
  • An inventory of devices on the network, including cameras and door controllers
  • Vendor and remote access accounts reviewed and removed when no longer needed

Not sure how many you can check? The free consultation and pen test answers that for you, or start with a cybersecurity assessment.

How Orange County clients get started

  1. Free assessment and pen test. We learn your environment and test 3 to 5 machines.
  2. Ranked roadmap. Findings are sorted into fix now, plan and monitor.
  3. Quick wins. MFA, email filtering and backup checks usually come first.
  4. Managed protection. MDR, patching and monitoring move to our 24/7 NOC/SOC.
  5. Testing and evidence. Recurring scans and tests show risk going down over time.
  6. Review. Regular reviews with leadership keep the plan current.

Testing frequency varies by client requirement and compliance scope. By default, BTI recommends monthly vulnerability scans and quarterly penetration tests. Financing at 3.99% is available for qualified buyers, subject to credit approval, for security hardware and projects.

If you are hit: what incident response looks like

  1. Contain. Affected devices and accounts are isolated so the attack stops spreading.
  2. Investigate. Logs and endpoint data show how the attacker got in and what they touched.
  3. Recover. Systems are cleaned or rebuilt and data restored from tested backups.
  4. Notify. We support your legal counsel and insurer with the facts they need, including for California breach notification.
  5. Harden. The gap that let the attacker in is closed, and the roadmap is updated.

Call your insurer first if you have cyber coverage, since many policies name the response firms you must use. We work alongside them.

Cyber Liability Essentials or Cyber Watch?

Both plans give you ongoing testing by our independent testing partner and reports that show risk going down over time.

Cyber Liability Essentials covers the baseline many insurers ask about. Cyber Watch is our pen testing plan for organizations that want testing on a regular schedule. Your engineer recommends one after the free pen test.

Details: compare the plans.

Security that works with your IT and your building

Security tools fail when no one owns them. Because BTI also runs IT support, the same team that patches your servers responds to alerts and fixes what a test finds. Clients who want both use managed IT in Orange County.

We also secure the cameras and door controllers we install, so building systems are not the weak link. See security cameras and access control in Orange County.

Download the 2026 Executive Guide to Managed IT and Cybersecurity (PDF).

Southern California service areas

BTI Communications Group, LTD. serves Southern California from our Santa Fe Springs office. Pick your region for local services.

Over 40 years of IT, security and communications work. Call 562-298-5000 or book a free consultation.

Get a free consultation

Cybersecurity in Orange County: questions we hear

Who provides cybersecurity services in Orange County?

BTI Communications Group, LTD. provides managed cybersecurity to Orange County businesses from its Santa Fe Springs office, including MDR, email security, identity protection, patching, backups and penetration testing with an independent testing partner, run through our 24/7 NOC/SOC.

What is included in the free consultation and pen test?

A working session with a BTI engineer on your risks and requirements, plus a credential-free Level 1 penetration test of 3 to 5 machines you choose, run with BTI's independent testing partner. You keep the report and the ranked roadmap. There is no cost and no obligation.

Does BTI have an Orange County office?

No. Our Southern California office is at 12155 Mora Dr in Santa Fe Springs. Security monitoring is delivered by our 24/7 NOC/SOC, and engineers drive to Orange County sites when needed. Call 562-298-5000.

How often should we run penetration tests and vulnerability scans?

Testing frequency varies by client requirement and compliance scope. By default, BTI recommends monthly vulnerability scans and quarterly penetration tests as part of ongoing security monitoring.

Can you help us complete our cyber insurance questionnaire?

Yes. We review what your carrier asks about MFA, endpoint detection and response, backups, training and incident response, show where you stand and close the gaps before renewal.

Do you help defense suppliers with CMMC?

Yes. CMMC and other compliance work is completed and contracted by BTI and its partners, including top industry professionals in each category.

What California laws affect our cybersecurity program?

Most California businesses need to consider CCPA and CPRA data protection rules and the breach notification law in Civil Code 1798.82. Customer contracts and industry rules may add more.

What does MDR do?

Managed detection and response watches endpoints and cloud accounts around the clock, investigates suspicious activity and isolates threats before they spread.

We already have an IT provider. Can BTI only handle security?

Yes. We can run security alongside your current IT provider or internal team, with clear ownership of each tool.

Is BTI's own security independently reviewed?

BTI follows ISO 27001 compliant governance, independently reviewed through the TAG ISO 27001 Compliance Program.

What should we do first if we think we have been hacked?

Disconnect affected devices from the network without turning them off, call your cyber insurer if you have coverage, and call your security provider. Do not pay a ransom or wipe systems before evidence is preserved.

How do we know if we are ready for a ransomware attack?

Check for MFA everywhere, endpoint detection and response, filtered email, tested offline or immutable backups, regular patching and a written incident plan. The free consultation and pen test shows where the gaps are.
Find out where your Orange County business stands

Book a free consultation and pen test. You keep the ranked findings and the roadmap.

  • Over 40 years in business
  • 400+ engineers
  • GSA contract holder (47QTCA21D00BA)
  • CMAS and TESMA contract awardee (California)
  • Licensed Alarm Company Operator, ACO #7670
  • C-7 License 807767
  • ISNetworld member
  • 24/7 NOC/SOC
  • ISO 27001 compliant
IT Services

Let's Start a Conversation

What's the best way for us to contact you?

Top quality brands, expert engineering, transparent cost, and measurable ROI.