Over 40 Years in BusinessISO 27001 compliantPublic sector: GSA contract holder

LA 562-298-5000 · Chicagoland 312-432-5300 · Phoenix 602-733-6807 · Client Support

Co-Managed IT Shared Responsibility Model

In co-managed IT, success depends on knowing exactly who is responsible for what. BTI’s Shared Responsibility Model gives you total clarity — so nothing falls through the cracks, security stays strong, and your documented, standards compliant execution is audit ready. 

co-managed-it-shared-responsibility-top

35+

Years of Proven Expertise

15+

Industries Served

10,000+

Alerts Handled, Zero Missed

98%

Client Retention Year After Year

Why Competitor's "Co-Managed IT" Providers Fail at Accountability

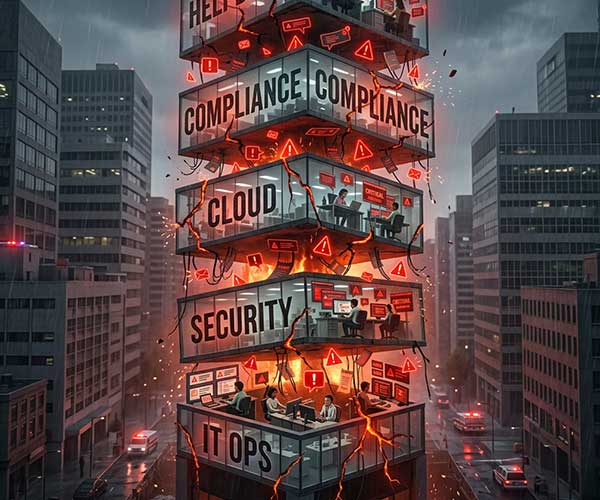
Most organizations believe they have a shared responsibility model — but in practice, responsibility is assumed rather than operationally defined. This fundamental disconnect creates dangerous operational gaps that expose enterprises to unnecessary risk and compliance failures.

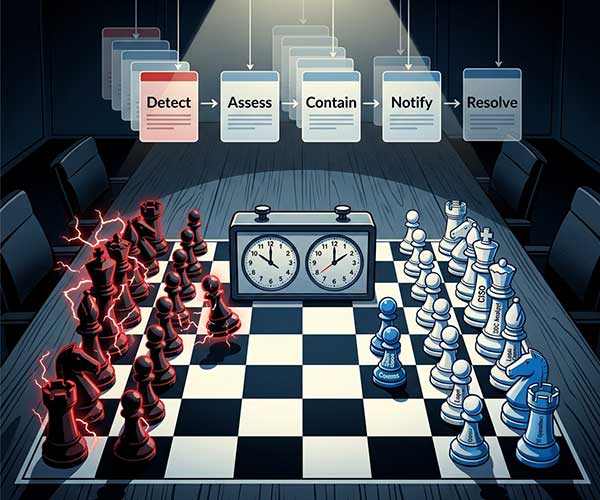
This creates critical gaps where security alerts are acknowledged but never acted upon, patching exists in documentation but remains inconsistently enforced across the environment, compliance controls are meticulously documented yet never properly validated, and incidents occur without any clear owner to drive resolution.

In regulated environments where oversight is constant and accountability is mandatory, undefined responsibility is not a flexibility — it’s a direct liability that can result in failed audits, insurance denials, and regulatory penalties.

BTI’s co-managed IT model exists specifically to eliminate this critical failure point through explicit documentation and operational clarity.
Assumed Ownership

No documented owner for critical security and infrastructure functions

Shared Tools

Technology deployed without clear operational responsibility

No Execution Authority

Unclear escalation paths and decisionmaking frameworks

co-managed-it-shared-responsibility

CORE FRAMEWORK

Shared Responsibility ≠ Shared Confusion

At BTI, shared responsibility is explicit, documented, and operational from day one. Every aspect of IT and security operations has a clearly defined owner, documented authority boundaries, and measurable accountability standards that survive audits, incidents, and leadership transitions.

icon5

Internal IT Ownership

icon 1

BTI Execution Ownership

diagnosis

Critical Principle

There is always a single accountable operator for every covered control – with documented authority to act, not just observe. Responsibility boundaries are defined before incidents, audits, or insurance reviews — not during them.

Responsibility Ownership by IT & Security Layer

Understanding who owns what is essential for operational success and audit readiness. This comprehensive breakdown eliminates ambiguity by mapping every critical IT and security capability to its designated owner, ensuring seamless execution and clear accountability at every layer of your technology stack.

CapabilityInternal ITBTI (Execution Owner)
End-User Devices & OSStrategic oversightMonitoring, patching, remediation
Servers & InfrastructureArchitecture approvalMonitoring, maintenance, incident response
Network, Firewalls, Wi-FiPolicy directionConfiguration, monitoring, firmware updates
RMM, NOC, SOC ToolingVisibility requirementsDeployment, tuning, daily operation
SIEM & Threat CorrelationStrategic awarenessIngestion, correlation, investigation
Incident ResponseBusiness decisionsDetection, containment, documentation
Compliance Controls & EvidenceExecutive accountabilityContinuous validation & evidence collection

This clear delineation ensures that every technology layer has an unambiguous owner for execution, while internal IT maintains strategic control and business alignment. The result is faster incident response, cleaner audits, and dramatically reduced operational friction.

Add AI and SaaS to the Responsibility Matrix

Almost every app growing businesses pay for now sells AI as an add-on, priced per seat, per credit or per token. Gartner predicts over 40% of agentic AI projects will be canceled by the end of 2027 because of escalating costs, unclear business value or inadequate risk controls (Gartner).

Through its co-managed IT services, BTI brings the AI you see (Microsoft Copilot, ChatGPT, Claude and Gemini, chat and voice agents) and the AI you don't (features inside your SaaS apps, background automations and our NOC/SOC partner's alert triage) into your real workflows, governed and cost-controlled:

  • Optimize consumption and cost: right-size Microsoft Copilot, ChatGPT, Claude and Gemini seats, tokens and credits, audit licenses and consolidate overlapping tools
  • Convert consumption into low-cost automation: turn expensive per-seat add-ons, tokens and credits into governed workflow automations you own, running on BTI's AI consumption management and workflow automation platforms
  • Govern it all: the AI tools, how they are used, and the enterprise systems they connect to
  • Guided Automation advisory included in every managed IT plan

Managed IT typically runs $60 to $290 per user per month, itemized. → Managed IT pricing

DECISION FRAMEWORK

Auditors and Insurers Don't Accept "Shared" — They Require Proof

Regulators, cyber insurance underwriters, and enterprise customers conducting third-party risk assessments do not evaluate good intentions or verbal commitments. They evaluate execution and evidence — and they expect both to be immediately available, consistently maintained, and independently verifiable.

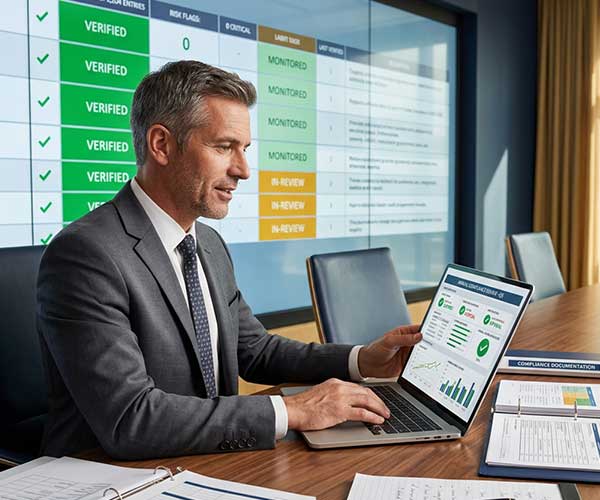
BTI’s shared responsibility model ensures that controls are continuously monitored rather than manually assembled before audits, evidence exists in real-time systems before auditors schedule their reviews, incident response activities are documented automatically as they occur, and insurance questionnaires map directly to operating controls that are already in place
and provable.

This approach eliminates the most common and most damaging compliance failure mode: “We thought someone else was handling that.”

co-managed-it-shared-responsibility2
icon4

Audit Ready

Evidence collected continuously, not
assembled reactively

icon9

Insurance Aligned

Controls map directly to underwriter requirements

icon8

Third-Party Defensible

Vendor assessments completed with documented proof

“The difference between passing and failing a cyber insurance renewal often comes down to one question: Can you prove your controls are operating? Not planned. Not documented. Operating.”

Co-Managed Does Not Mean Co-Overworked

One of the most persistent myths about co-managed IT is that it simply adds more work to already overwhelmed internal teams. BTI’s model operates on the opposite principle: internal IT should be strategic, not buried in operational execution.

Before BTI

Internal IT manages strategy, execution, monitoring, remediation,
and evidence — often after hours and on weekends

After BTI

Internal IT focuses on business alignment and strategy, while BTI handles operational load and after-hours coverage

What Internal IT Teams Are NOT Asked to Do

How BTI Operates in Practice

one-green-circle

Helpdesk for Internal IT

BTI serves as an extension of your team, handling operational requests and execution work

two-green-circle

Project Execution Team

Infrastructure upgrades, migrations, and security implementations managed end-to-end

three-green-circle

Escalation & After-Hours Layer

24/7 monitoring, threat response, and incident management without internal IT burnout

Result: Internal teams stay focused on business-critical initiatives while BTI handles the operational load that traditionally causes turnover and burnout.

This Model Works Best When…

BTI’s shared responsibility model is purpose-built for regulated and security-conscious enterprises facing specific operational and compliance challenges. This approach delivers maximum value when your organization matches one or more of these critical profiles.

You Have Internal IT But No Internal SOC

Your team understands the business and manages technology strategy, but lacks the specialized resources, 24/7 staffing, and security expertise required to operate a Security Operations Center.

Compliance Must Be Provable, Not Implied

You operate in a regulated industry where auditors, insurers, and customers demand continuous evidence of control effectiveness — not periodic self-assessments or documentation alone.

Tools Exist But Are Underutilized

You’ve invested in RMM platforms, SIEM tools, endpoint detection, or other security technology, but lack the dedicated staff to tune, monitor, and operationalize these systems effectively.

Accountability Must Survive Audits and Incidents

Your leadership, board, or insurance carrier requires clear documentation of who owns what — and that accountability structure must hold up under regulatory scrutiny and post-incident reviews.

If your organization is navigating these challenges, BTI’s co-managed model provides the operational backbone and documented
accountability that transforms IT from a cost center into a strategic asset.

Define Responsibility Before It Becomes a Risk

The time to establish clear accountability is before an incident occurs, before an audit is scheduled, and before an insurance renewal is denied. BTI’s shared responsibility model provides the operational clarity and documented proof that regulated enterprises require.

Whether you’re preparing for compliance reviews, managing cyber insurance requirements, or simply trying to reduce internal IT burnout, the next step is understanding how this model applies to your specific environment.

co-managed-it-shared-responsibility-3

Governance & assurance

Compliance Governance, Certifications & Partner Assurance

BTI Governance & Verified Qualifications

BTI maintains an internal ISO 27001 compliant governance program and continuously improves its information security, vendor management, and operational controls with third-party validation. Held by BTI: ISO 27001 compliant (Technology Assurance Group) · Microsoft Partner · Cisco Select Partner and Cisco SMB Blackbelt · Axis Gold Partner · Kantech Global Edition Certified Partner Platforms we install and support: Cisco, Cisco Meraki, Axis Communications, Avigilon, Microsoft, Milestone, Brivo, Kantech and Avigilon Alta (formerly Openpath).
ISO 27001 compliant badge by Technology Assurance Group (TAG) for BTI

Partner Certifications, Audits & Compliance-Aligned Platforms

BTI works with compliance-aligned data centers, cloud platforms, monitoring providers, payment processors, cybersecurity vendors, and service partners that maintain independent certifications, audits, attestations, or compliance programs such as UL, PCI, SOC 2, SOC 3, GDPR support, and other framework-specific controls.

Held by the platforms and providers BTI resells or uses

BTI 24/7 NOC/SOC
SOC 3 report held by BTI's data center and cloud providers
HIPAA-aligned hosting from BTI's cloud and data center providers
PCI DSS compliance held by payment processors BTI uses
UL 827 listing held by BTI's alarm monitoring provider
GDPR support from BTI's cloud platform providers
FedRAMP authorization held by cloud platforms BTI resells
FISMA compliance held by cloud platforms BTI resells
ISO 14001 held by BTI's data center providers
ISO 50001 held by BTI's data center providers

These certifications, audits and attestations belong to the third-party platforms and providers, not to BTI. Which ones apply depends on the specific platform, service, data center, processor, monitoring provider, or vendor used in your solution. Ask us which apply before you buy.

Why Organizations Choose BTI

Organizations operating in regulated or converged environments choose BTI for infrastructure-led execution that reduces risk and
operational burden.

integrations

Infrastructure-led execution

enhanced security

Continuous compliance proof

scalability

Converged IT, cyber, VoIP, and physical security

icon3

Transparent, itemized costs and management visibility

Related IT Services

Related Articles

Ready to Eliminate Accountability Gaps?

BTI’s co-managed IT shared responsibility model is built for organizations that cannot afford ambiguity in their IT and security operations. If your enterprise requires audit-defensible accountability, continuous compliance evidence, and operational reliability without internal team burnout, it’s time to explore how this framework can transform your technology operations.

24/7

IT Engineers

Continuous operations without internal staffing burden

100%

Control Documentation

Every capability has a defined owner and evidence trail

<15min

Incident Response

Average time to initial containment for critical threats

IT Services

Let's Start a Conversation

What's the best way for us to contact you?

Top quality brands, expert engineering, transparent cost, and measurable ROI.